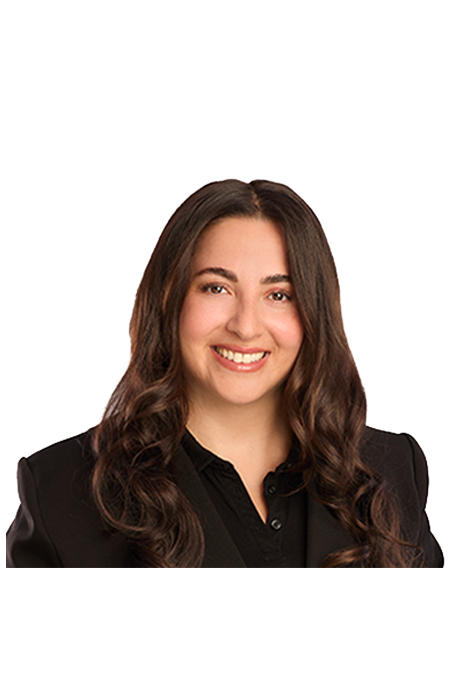
Tulin Sevgin

Head of NSW
Tulin Sevgin is the Head of NSW leading regional cyber security advisory, architecture, and sovereign managed delivery across New South Wales.
Talk to an expert
Highlights

Career highlights

‍

Tulin Sevgin is the Head of NSW at Cythera, a Bastion Security Group Company, leading regional cyber security advisory, architecture, and sovereign managed delivery across New South Wales. She leads the expansion of Cythera’s regional delivery footprint following its integration into the wider trans-Tasman group.  

Tulin brings extensive leadership experience in establishing and scaling high-performing cyber security and risk practices across Australia. Prior to joining Cythera, she was an inaugural recruit and Practice Lead at MinterEllison, where she built and grew the firm's national cyber advisory and risk assurance capabilities from inception into a multi-million-dollar practice. Across a career dedicated to governance, risk, resilience, and executive advisory, she has partnered with boards, CISOs, and public sector leaders across financial services, critical infrastructure, and government to solve complex digital trust and operational challenges.  

Outside of work, Tulin is an avid tennis player, keen angler, and dedicated coffee lover. When she isn’t exploring Sydney’s coffee scene or spending time outdoors, she can usually be found unwinding with a good manga series.

Cyber security news

Latest advisories

Stay ahead of emerging threats with our expert blog posts, research, and industry updates.
Silverstripe - Host Header Injection
Silverstripe CMS is affected by a Host Header Injection flaw, which can be exploited to manipulate password reset workflows, potentially redirecting or compromising user data.
FarCry Core Framework - Multiple Issues
FarCry Core contains multiple vulnerabilities that could let unauthenticated users upload arbitrary files and execute remote code on the hosting server.
Silverstripe – Cross-Site Scripting (XSS) Vulnerability
With local organisation admin credentials, an attacker can exploit the API to create, delete, or revert virtual machine snapshots in other organisations’ Virtual Data Centres (VDCs), breaching isolation boundaries.
Discover our services

We have the tools to pinpoint risks

Whether it’s hidden vulnerabilities or patterns you might miss, we help you stay one step ahead and make confident, informed decisions. Understand how our services can help your business uncover critical risks

Talk to an expert
Employee Cyber Training & Awareness
Your people are your first line of defence. Our cyber training builds awareness sharpens instincts and turns everyday staff into assets.
Advisory
When clarity is critical and stakes are high, our advisory services deliver strategic, executive-level security expertise that empowers decision-making and resilient operations.